Wednesday, January 10, 2007
Eyes in London's Sky - Surveillance Poster
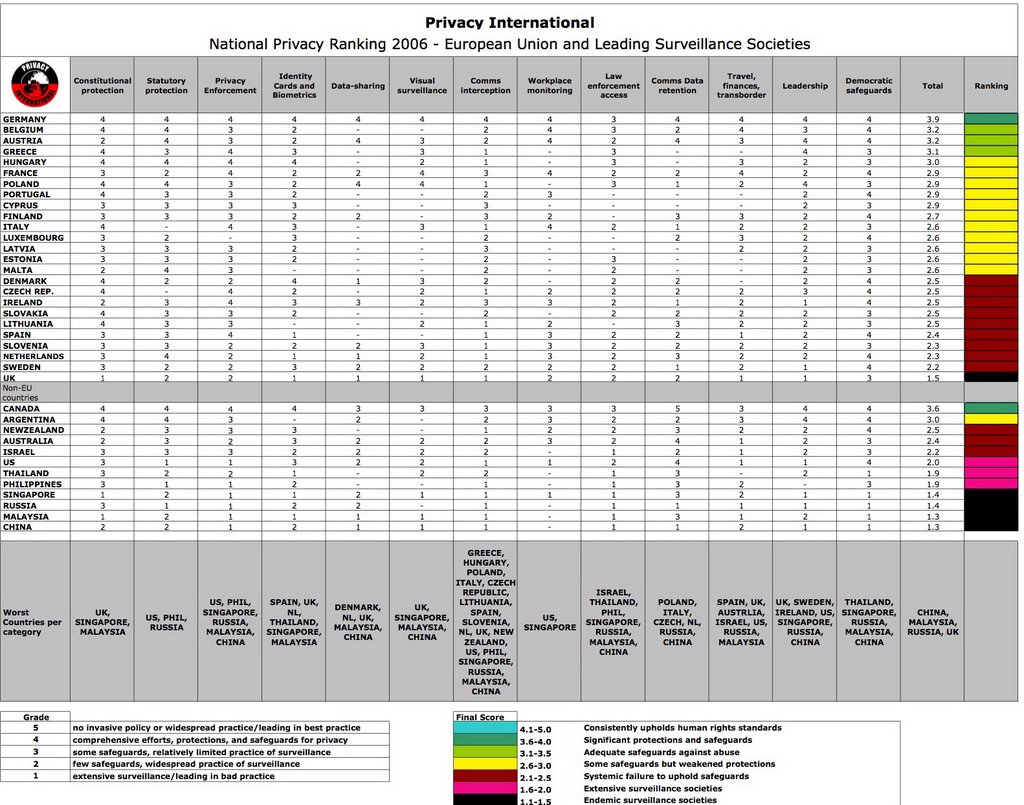
Alcohol's bad, drugs are bad, surveillance is good for protecting your from the insecurities we made you become paranoid of, and so are head-mounted surveillance cams equipped police officers. Sure, but consider the social implications too. London may be one of the most important business centers in Europe -- next to Frankfurt and Rotterdam -- but I'm so not looking forward to living in what's turning into a synonym for 1984.

Tuesday, January 09, 2007
Still Living in the Perimeter Defense World
Whereas you'd better break out of the budget-allocation myopia and consider prioritizing your security investments, decreased spending on information security in certain regions means good old-fashioned malware and spam floods for the rest of regions doing it :
"Fewer small- and medium-sized enterprises (SMEs) in Taiwan will increase their spending on information security this year compared with last year, according to a report released Thursday by the Institute for Information Industry's Market Intelligence Center (MIC). The report said that only 12.9 percent of SMEs will increase their information security spending in 2007, compared with 16.2 percent in 2006."
Perimeter defense and host security is like the ABC of security, but since viruses and network attacks are "taken care of" all seems fine -- you wish.
"While more than 90 percent of SMEs have installed anti-virus software and firewall devices, only 11 percent have installed unified threat management products, according to Wang."
And while your organization is multitasking on how to budget with the anyway scarce resources due to legal requirements to do so, or visionary leaders realizing the soft and hard cash losses if you dare to pretend your organization wouldn't get breached into, regions around the world don't have the incentives to do so. If you bring too many people to a party someone always takes a *** in the beer, or so they say. Know when to spend, how much, on what, and is the timing for your investment the right one given the environmental factors of your company. A small size business doesn't really need a honeyfarm unless of course the admin is putting a personal effort in the job.
Data Mining Credit Cards for Child Porn Purchases
 22 million customers had the privacy of their credit card purchasing histories breached for the sake of coming up with 322 suspects while looking for transactions to a single child porn web site - ingenious, absolutely ingenious :
"In the case under investigation, police were aware of a child pornography Web site outside of Germany that was attracting users inside the country. And they asked the credit-card companies to conduct a database search narrowed to three criteria: a specific amount of money, a specific time period and a specific receiver account."
I don't want to ruin the effect of the effort here, but why do you still believe child porn is located on the WWW, in the http:// field you're so obsessed with? Is the WWW the only content distribution vector for multimedia files you're aware of? Try the Internet Relay Chat, the concept of Fserve to be precise. Having found the low lifes who buy child porn over the Web is like picturing a pothead as the über-dealer to meet your quotas, namely, efforts like these have absolutely no effect on the overal state of child pornography online. It's the wrong way to fight the war. Put the emphasis on fighting the very production process -- trafficking of children -- not the distribution one.
Insider Sentiments around L.A's Traffic Light System
 Rember how the Hollywood Hackers were winning time while heading straight to Grand Central Station in NYC to outsmart the Plague's plan to cause a worldwide ecological disaster and cash in between? In pretty much the same fashion -- without the randomization of traffic lights -- two engineers in between their union's strike seems to have watched the movie too :
"They didn't shut the lights off, city transportation sources said. Rather, the engineers allegedly programmed them so that red lights would be extremely long on the most congested approaches to the intersections, causing gridlock for several days starting Aug. 21, they said."
Whether overal paranoia due to the sensitive nature of the workers' positions and the publicly stated intentions, insider sentiments prevail from my point of view.
Monday, January 08, 2007
Iran Bans Purchase of Foreign Satellite Data
 Re-inventing the wheel :
"According to the bill, a copy of which has been sent to all ministries, organizations, state and revolutionary institutions, the purchase of information from foreign sources is deemed against the law. Specialists of the Defense Ministry have currently succeeded in initiating a project for obtaining satellite information online. For the first time in Iran, it is now possible to produce topographic maps, on a scale of 1/10,000, of a specific area for municipal and developmental projects, with the satellite images of very high resolution."
Guess they don't want others to know which locations of their country are still unknown to themselves, but with the bill definitely implemented as a national security measure, and to improve the nation's self-esteem, drop a line if they ever get close to producing such high-resolution image of their Natanz facility on their own.
Russia's Lawful Interception of Internet Communications
 Don't fool yourself, they've been doing it for the time being, now they're legalizing it -- working for anything like the EFF in Russia means having the bugs in your place bugged. Citing Cyber-Terrorism Threat, Russia Explores Internet Controls :
"An estimated 20 percent of the Russian population now has access to the Internet. Whereas the Putin administration exerts tight control over the major domestic broadcast and print media, it does not currently restrict the content of Internet sites on a wide scale. Web sites such as Gazeta.ru and Lenta.ru provide many of the articles and commentary that would normally otherwise appear in an opposition press. Several wealthy Russians living in political exile, including Boris Berezovsky and Vladimir Gusinsky, own Russian-language websites that publicize their anti-Putin views to Russian audiences. In August 2006, Russian right-wing extremists used the Internet to coordinate a bomb attack against illegal migrants from Asia."
Give me an excuse for data retention? No, give me another one besides the infamous "if you don't have anything to hide then why worry"? We all have things to hide, and things we don't want others to know, that's still called my privacy, and since when does this became a terrorist activity, or someone's just piggybacking on the overall paranoia created by the thought to be acting as government watchdog, media -- don't be a reporter, be a journalist! Winning the public support in different countries largely relies on the local attitudes towards the key buzzwords - terrorists are using the Net as a "safe heaven", and child pornographers are operating online, while people are unemployed and primitive deceases which should been dealth with years are a second economic priority, next to your first one - fighting your (political campaign) demons, or the (upcoming budget allocation) demons you put so much efforts into making me believe in. Start from the basics, why retain everyone's data, and intercept everyone's communications while forgetting that information is all about interpretation? How come you're assuming -- if you're even considering it -- that such a neatly centralized databases of private information would be protected from insiders, even outsiders which will inevitably be tempted to having access to such a database? A country's intelligence is the government's tool for protecting the national security or beyond, but over-empowering the watchers is so shortsighted, you'd better break through your black'n'white world only and start considering all other colours as equal. Don't slip on your values.
If you sacrifice privacy for security, you don't deserve both of them, and the utopian idea of having a 100% successful law enforcement as the panacea of dealing of crime reminds of a quote I recently find myself repeating very often - make sure what you wish for, so it doesn't actually happen.
Sunday, January 07, 2007
Visits to the White House Now Top Secret Information
 Informative - White House visitor logs declared top secret :
"The five-page document dated May 17 declares that all entry and exit data on White House visitors belongs to the White House as presidential records rather than to the Secret Service as agency records. Therefore, the agreement states, the material is not subject to public disclosure under the Freedom of Information Act.
In the past, Secret Service logs have revealed the comings and goings of various White House visitors, including Monica Lewinsky during the Clinton administration."
I thought that's always been the case anyway, but it closes a loophole that could result in potentially embarrassing future developments -- or less accountability. Time will show. More info.
Sunday's Portion of Hahaha
 While patiently waiting for the future adventures of Monica Furious, I came across a nice collection of cartoons. I'm sure you'll find these two very entertaining - "The Disabled Cookies" and "The Spam Prison".
Web Economy Buzz Words Generator
 Whether looking for VC cash, or having a quota to meet being a salesman, some of these may come handy or pretty much make someone's morning.
Here are my favorite:
e-enable integrated mindshare
empower impactful infomediaries
architect compelling ROI
productize 24/7 e-services
recontextualize compelling ROI
Doesn't matter how well you project your success, if you don't have an elevator pitch worth someone's attention span, than you don't know what you're doing, but marely relying on the web economy's state of buzziness -- this is another one. Try some copywriting exercises too.
Four Years of Application Pen Testing Statistics
 Invaluable :
"The article presents a unique opportunity to take a peek into the usually secluded data regarding the actual risk posed to Web applications. It shows a constant increase in risk level over the four years and an overwhelming overall percentage of applications susceptible to information theft (over 57%), direct financial damage (over 22%), denial of service (11%) and execution of arbitrary code (over 8%). The article analyzes results of first time penetration tests as well as repeat tests (retests) in order to evaluate the evolution of application security within Web applications over time."
Lots of figures respecting your busy schedule, and the authors' data pointing out how the lack of repeated testing, and the "security as a one time purchase" mentality, actually means a false sense of security. Having a secured web application doesn't mean the end user won't be susceptible to a client side attack, and having a secured end user doesn't mean the web application itself will be secured, ironic, isn't it? Perhaps prioritizing the platforms to be audited, namely the major web properties, could protect the always unaware end user to a certain extend -- from himself. Related comments.
Foreign Intelligence Services and U.S Technology Espionage
 Talking about globalization, like it or not, perceive it as a threat to national security or a key economic benefit, it's happening and you cannot stop it. Nothing else will add more long-term value to a business or a military force than innovation, and when it comes to the U.S military's self-efficiency in R&D, it's pretty evident they've managed to achieve the balance and still dictate the rhythm.
The methods used aren't nothing new :
"The report says that foreign spies use a wide variety of techniques, ranging from setting up front companies that make phony business proposals to hacking computers containing information on lasers, missiles and other systems. But the most popular methods of attempting to obtain information was a simple “informational request” (34.2%) and attempts to purchase the information (32.2%). Attempts were also made using personal relationships, searching the Internet, making contacts at conferences and seminars, cultural exchanges."
What's new is the actual report in question - "Technology Collection Trends in the U.S. Defense Industry". OSINT is also an important trends gathering factor, and so is corporate espionage through old-fashioned malware approaches or direct intrusions, and it's great the report is considering the ease of execution on these and the possible network vulnerabilities in the contractors :
"DSS also anticipates an increase in suspicious internet activity against cleared defense contractors. The potential gain from even one successful computer intrusion makes it an attractive, relatively lowrisk, option for any country seeking access to sensitive information stored on U.S. computer networks. The risk to sensitive information on U.S. computer systems will increase as more countries develop capabilities to exploit those systems."
Then again, what's produced by the U.S but cannot be obtained from there, will be from other much more insecure third-party purchasers -- how did Hezbollah got hold of night vision gear? Or even worse, by obtaining the leftovers from a battle conflict for further clues.
The bottom line question - is the illegal transfer of U.S technology threat higher than the indirect leakage of U.S educated students taking their IQ back home, while feeling offended by their inability to make an impact were they a U.S citizen?
Thursday, January 04, 2007
Technical Analysis of the Skype Trojan
 During December yet another trojan started making rounds, this time dubbed the Skype trojan -- SEO conspiracy. Was the trojan exploiting a zero day vulnerability in the Skype protocol? Absolutely not, as it was basically using Skype's messaging service as a propagation vector, thus, the gullible and in a Christmas mood end user was still supposed to interact with the malware by clicking on the link. And with required end user's interaction, the possibilities for major outbreaks were very limited. Perhaps the only development worth mentioning is the malware author's use of commercial anti-cracking software -- NTKrnl Secure Suite -- to make the unpacking harder, or at least theoretically improve the time needed to do so compared to using publicly obtainable, and much more easily detectable packers.
Two days ago, Nicolas Brulez from Websense Security Labs released a technical analysis of the trojan itself, and here's your proof for the logical possiblities of specific copy'n'paste malware modules :
"The main protection scheme I faced was the copy pasted from my Honeynet Scan of The month 33 Challenge. The breakpoint detection was 100% identical, even the numbers I had generated randomly. More importantly, the technique I had written based on SEH + cpuid/rdtsc was also copied. The only difference was that they used the EDX register to compare the timing.
Copy pasting protection code without even changing it a little, provides no security at all and allowed me to unpack it even quicker. (gotta love looking at code you wrote 2 years ago)
It apparently included some other tricks, that made it a little harder to unpack, and the file looked like it was corrupted at some point. In order to debug it and comment my disassembly in a readable way, I opted to use a userland debugger, and thus had to write a little shellcode for injection into the packed malware. Basically, it entailed abusing Windows Exception Handling (using a hook), to get past every check. After that, one could attach his favorite userland debugger to the malware and eventually find the Original Entry Point. Although the imports rebuilding for this protector isn't hard at all, it wasn't mandatory in this executable as it only imported one function: ExitProcess"
And while the average malware coder is using commercial tools to make his releases harder to analyze, the almighty jihadist is still living in the Hacker Defender world.
Were you Tracking Santa's Location?
 As usual, NORAD were, but there's one minor issue to keep in mind and that's how during the Christmas and New Year holidays Santa Claus is the most successfully targeted victim of identity theft. Hopefully they were tracking the real Santa through the real Rudolph as the weakest link :
"The satellites have infrared sensors, meaning they can detect heat. When a rocket or missile is launched, a tremendous amount of heat is produced - enough for the satellites to detect. Rudolph's nose gives off an infrared signature similar to a missile launch. The satellites can detect Rudolph's bright red nose with practically no problem. With so many years of experience, NORAD has become good at tracking aircraft entering North America, detecting worldwide missile launches and tracking the progress of Santa, thanks to Rudolph."
All rest is a commodity but attitude.
Tuesday, December 19, 2006
Phishing Domains Hosting Multiple Phishing Sites
 Well, well, well. What do we got here? Couple of interesting domains hosting phishing sites of multiple banks for you to take a look at, or at the cached versions to be precise. What's worth mentioning is the rise of phishing sites using the much more easily and anonymously registered .biz ; .info ; .name domains. However, the first part of these is related to 211.137.13.131 :
baldwindy.name
leqwas.biz
noosfo.biz
rsytarai.biz, another one
Multiple hosting:
201.195.156.13
lugers.biz
loreta.biz
tuker.info
Now, try searching the entire .biz space for "Bank Austria Creditanstalt". The good news is that even the average anti-phishing toolbar is capable of detecting these. The bad news is that customers aren't currently using such toolbars as much as they should. And with phishing toolkits lowering the entry barriers in this space by making it easy for wannabe phishers to "make an impact", we've got an efficient problem to deal with.
Google and Yahoo's Shareholders Against Censorship
 Collective bargaining tends to achieve the necessary echo effect :
"The New York City Pension Fund wants shareholders to force Google and Yahoo to refuse Internet censorship requests by governments. The fund, which owns nearly $280 million worth of Google shares and $110 million in Yahoo shares, filed resolutions for shareholders at the two Internet companies to vote on at the next shareholder meetings. The resolution states that U.S.-based technology companies "that operate in countries controlled by authoritarian governments have an obligation to comply with the principles of the United Nations Declaration of Human Rights."
Go, go, go, shareholders. So that by the time censorship ends up where it's most aggressive for the time being, we can feel proud of ourselves living in a World 2.0, a world in which we all have universal access to the collective wisdom of everyone. Wait, that used to be part of both, Google's and Yahoo's mission statements once. From another perspective, the companies themselves have their hands tied by the overal Western world's revenues generation greed, and outsourcing inspirations in China's booming economy. But pretending it isn't happening is like ignoring the existence of the thought police these days.
Monday, December 18, 2006
Le Cyber Jihad
It's very nice to see that Marc Olanié is still keeping track of my articles. Here are several more worth Babelfishing.
Thursday, December 14, 2006
Top Ten Scams of 2006
 ConsumerAffairs.com did a great job in summarizing the top 10 scams of 2006 "from the roughly 50,000 consumer complaints we've processed in the past year". Here's what the gullible consumer complains about :
01. Fake Lottery Scam
ConsumerAffairs.com reported on one case in which an elderly Kansas man lost over $300,000. You should have Asked Merrill to point you to the "tickets" with the highest probability of success, but it's too late for you now. Baby booming gullibility in action.
02. Phishing-Vishing Scams
I'm very surprised it's the second and not the first complain, but how come? Consumers aren't even aware they got scammed at the first place. Do yourself a favour, and don't discuss your financial details with automated systems. Think before you act, it's like deciding whether to enter a singles bar or not.
03. Phony Job Scam
"Any employment offered online without a formal interview, no matter where it originates, should be treated with skepticism," said Arkansas Attorney General Mike Beebe, who investigated one of these scams in 2006. Thank you, you've just ruined the entire virtual telecommuting concept. I'm aware of another type of scam where fake job postings seek to harvest as much personal information from applications as possible. Other practices are also used.
04. Negative Option Scams
Look for the ASTERISKS, it should be somewhere around the FREE proposal.
05. Nigerian 419 Scams
People falling into this one, are the type of people suffering from the "rich-uncle complex". You don't know his exact wealth, but you secretly hope that on a sunny day a handsome, and of course charging by the minute laywer will bring the news you've been subconsciously expecting your entire life. Think for real and forget about the Internet. Would a complete stranger offer you millions of dollars because he has no one else to give the money to, or cannot open up a bank account for themselves?
06. Pump & Dump Scam
Rainer Böhme and Thorsten Holz evaluated the situation.
07. Bogus Fuel Saving Devices
Make an analogy with washing powder/tablets/liquid who's actively advertised as an "energy saver" due to its sophisticated technology that doesn't require hot water, when it happens to be a commodity and if you're going to be saving energy from it, then you've either watched a movie about the Third World, or are very desperate.
08. Grandparents Scam
An elderly person is targeted by the scammer who calls and says something like, "It's me, grandpa." The elderly person will respond, thinking it's one of their grandchildren. Unbelieavable, and perhaps another reason to keep in touch with your grand-parents more often, so they could at least recognize your voice.
09. Oprah Ticket Scam
In case you fall victim into this one, you're not just bored to the bottom of your brain, but a potential guest at Oprah's show with the unique ability to explain how this scam ruined your life, but later on helped your meet the person of your life, where else if not in an online scam discussion group. I feel you.
10. craigslist Scam
It's like the Yellow Pages, some postings are so automatically generated that they happen to be a waste of time, but hopefully not money, so be aware.
Terrorism Cartoon Contest
 Why is it that even with my extemely well developed sense of black humour, I'm still not laughting? Here's another contest collection, again hosted by Iran, this time on the denial of the Holocaust. Thankfully, my history teacher taught me otherwise, and the No Such Agency folks have the complete coverage in their indispensable "Eavesdropping on Hell : Historical Guide to Western Communications Intelligence and the Holocaust 1939-1945".




Tuesday, December 12, 2006
BuzZzZ Generation
Just a few of the sites/blogs that have recently featured my posts exposing the low lifes :
- Linuxsecurity.com - "Analysis of the Technical Mujahid - Issue One" ; "Current State of Internet Jihad"
- Informit.com - "How do terrorists spell rootkit in Farsi?"
- Defensetech.org - "Rapid fire 1" ; "Rapid fire 2"
- Net-security.org - "Analysis of the Technical Mujahid - Issue One"
- Cyberia.org.il
Interested in knowing how was Al Qaeda using the Internet before 9/11 with all the multimedia released back then? Moreover, have you ever wanted to take a peek at some of the most recent tools-of-the-trade malware authors use on a daily basis? Stay tuned for the Christmas Full Disclosure Series summarizing some of my recent findings, and beyond!
Share your knowledge. It's a way to achieve immortality. Dalai Lama
Subscribe to:
Posts (Atom)
About Me
- Dancho Danchev
- Independent Security Consultancy, Threat Intelligence Analysis (OSINT/Cyber Counter Intelligence) and Competitive Intelligence research on demand. Insightful, unbiased, and client-tailored assessments, neatly communicated in the form of interactive reports - because anticipating the emerging threatscape is what shapes the big picture at the end of the day. Approach me at dancho.danchev@hush.com

Dancho Danchev's Blog - Mind Streams of Information Security Knowledge is wearing HalfBaked. Free WP-Theme by GuyFisher. Converted to Blogger by Template-Godown.